ISO 27001 certification

Get ISO 27001 certified without building a security team first.

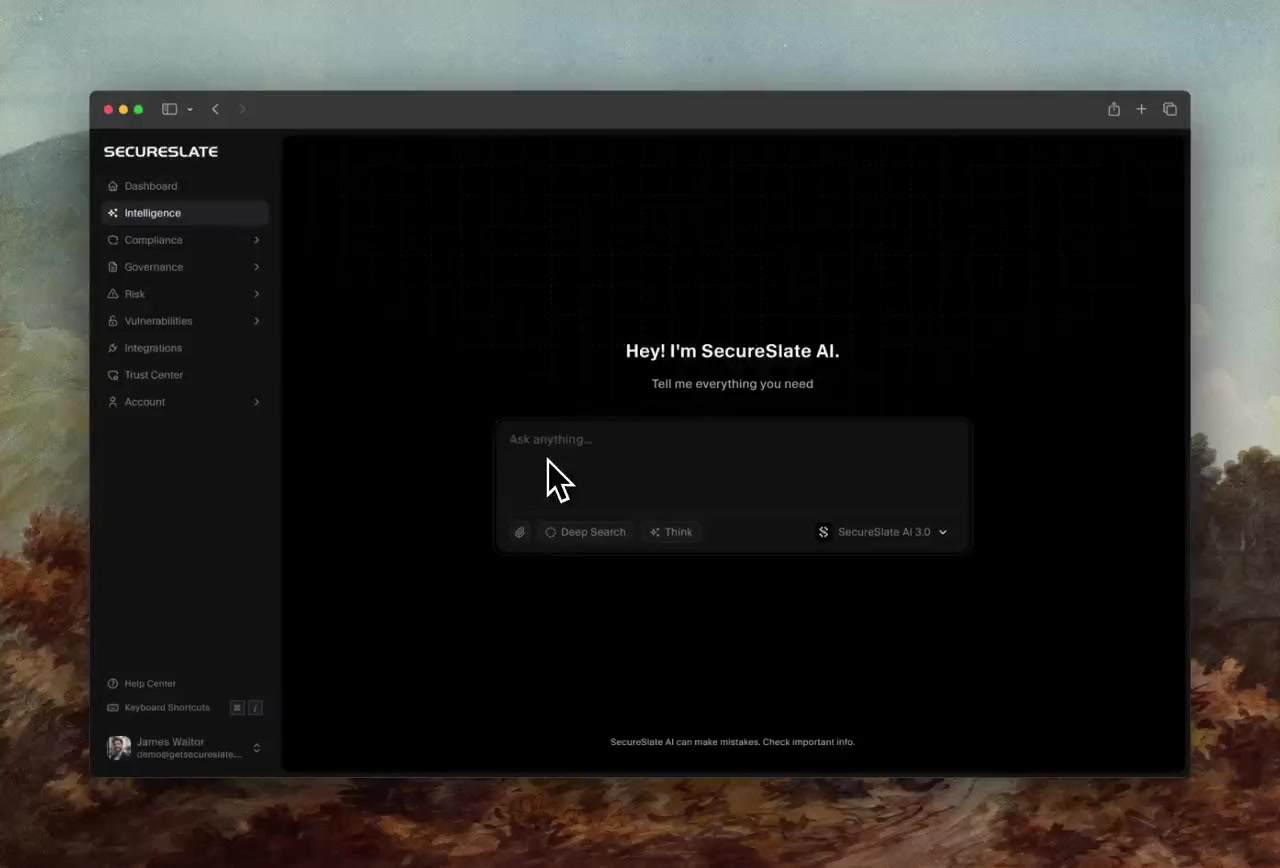
European and enterprise buyers expect ISO 27001. A dedicated SecureSlate compliance lead builds your ISMS with you, our compliance automation platform collects evidence from the tools you already use, and one fixed price covers the work from scoping call to certificate.

Annex A, ISO 27001:202293 controls

Annex A, ISO 27001:2022: 93 controls, 37 Organizational, 8 People, 14 Physical, 34 Technological. 11 highlighted: Evidenced by included security scanning.

Evidenced by included security scanningScoped with your compliance lead
Current version
ISO/IEC 27001:2022
Certificate
Valid for 3 years, audited every year
Typical audit readiness
2–5 weeks
The standard

ISO 27001 certification audits how you run security, not which tools you bought.

ISO/IEC 27001:2022 has two halves, and an accredited auditor tests both across a three-year cycle.

A management system that actually runs

Clauses 4 to 10 define the ISMS: a documented scope, leadership commitment, a risk assessment and treatment plan, security objectives, internal audits, management reviews, and corrective action. Auditors look for records showing that cycle happens, not a policy promising it will.

93 Annex A controls, each one justified

Annex A groups 93 controls into four themes: 37 organizational, 8 people, 14 physical, and 34 technological. You do not implement all of them, but your Statement of Applicability has to explain every inclusion and exclusion against your risk assessment.

A three-year certificate, audited every year

Certification starts with a Stage 1 review of your documentation and a Stage 2 audit of how controls operate in practice. The certificate lasts three years, with surveillance audits in years two and three and a recertification audit before it expires.
How it works

We build your ISO 27001 ISMS with you, then keep it running between audits.

Four stages from the scoping call to a certificate, with a named compliance lead accountable at every one.

Scope and gap analysis

We define what the certificate will cover: products, locations, teams, and the cloud and SaaS providers your data passes through. Your compliance lead then measures where you stand against every clause and Annex A control and gives you a dated plan with named owners.

Build the ISMS

We run the risk assessment with your team, write the treatment plan, draft policies for how your company really operates, and produce the Statement of Applicability. Integrations connect to your cloud, identity provider, code host, and devices so evidence collects itself.

Operate it before the auditor arrives

An ISMS has to show it runs. We complete the internal audit and management review that certification bodies expect to see before Stage 2, close any nonconformities, and switch on continuous monitoring so controls stay in place while you wait for audit dates.

Certification, then every year after

We coordinate with the accredited certification body you choose, prepare evidence for Stage 1 and Stage 2, and stay with you through fieldwork. After certification, the same program carries you into surveillance audits and recertification instead of a rebuild each year.
What is included

Everything your ISO 27001 auditor samples, prepared before they ask.
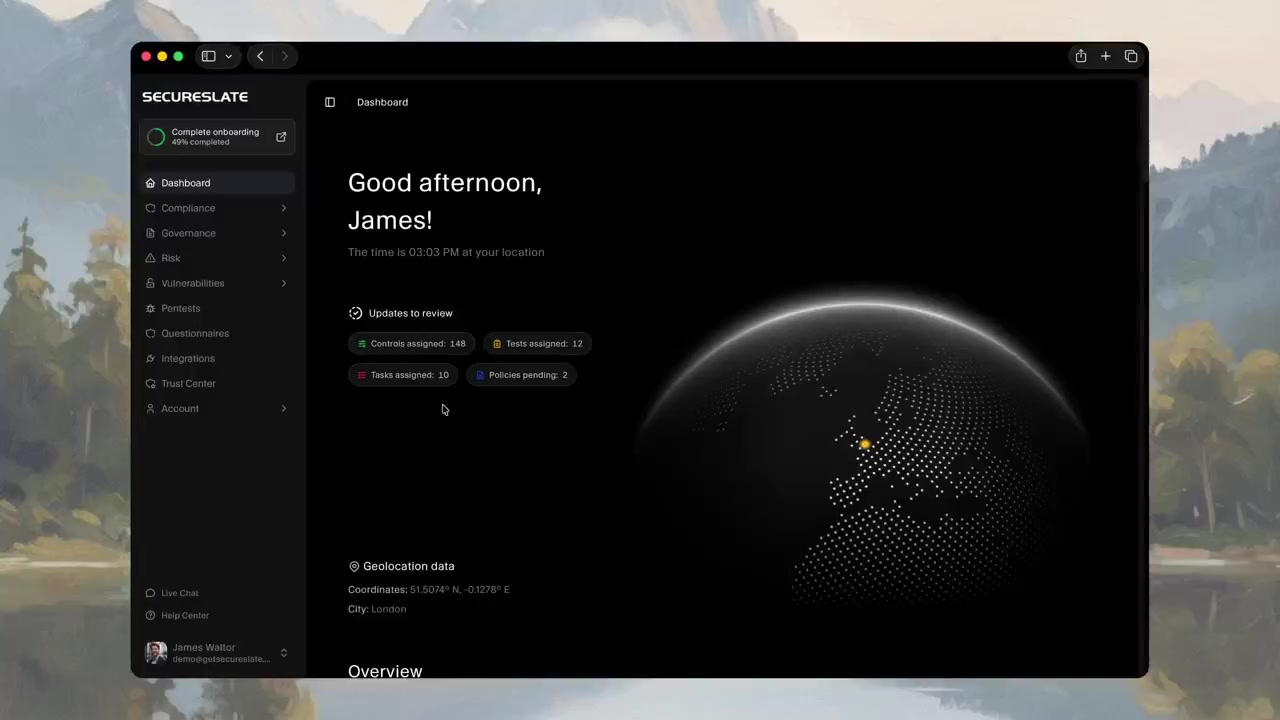
ISO 27001 compliance software and the expert who runs it arrive together under one fixed price, so the program does not land on your engineers.

A dedicated compliance lead

One experienced practitioner owns your ISO 27001 program end to end. They run the risk workshops, draft the documentation, work in your Slack, and answer the certification body directly, so your team reviews and approves instead of learning the standard.

Risk assessment and treatment plan

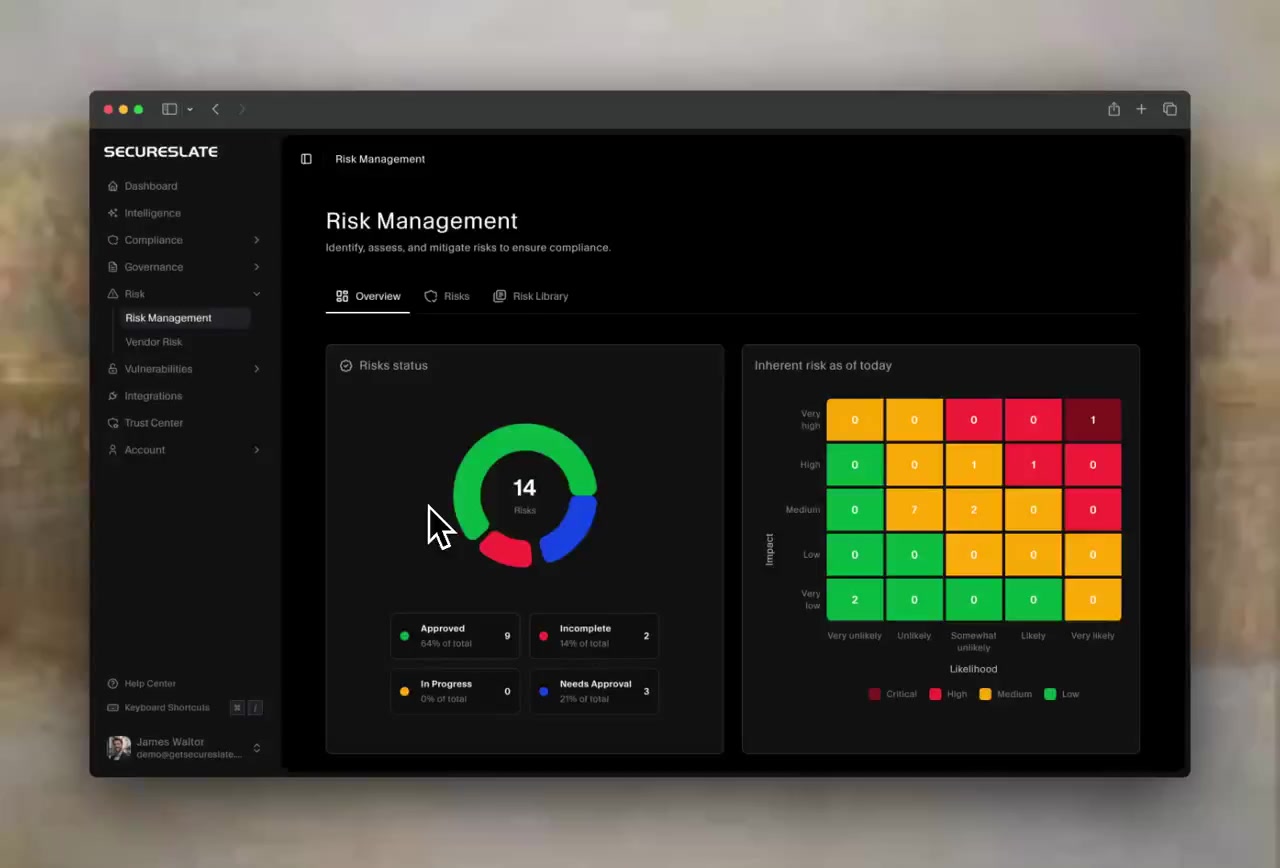
Assets and threats scored against criteria you agree, with a treatment decision and an owner recorded for every risk. You get the documented assessment and treatment plan that clause 6 requires, kept current as your business changes.

A Statement of Applicability that stays true

Every Annex A control marked included or excluded, with a justification traced back to your risk assessment. We draft it, you approve it, and we update it as controls change, which is where most SoAs go stale between audits.

Evidence from the stack you already run
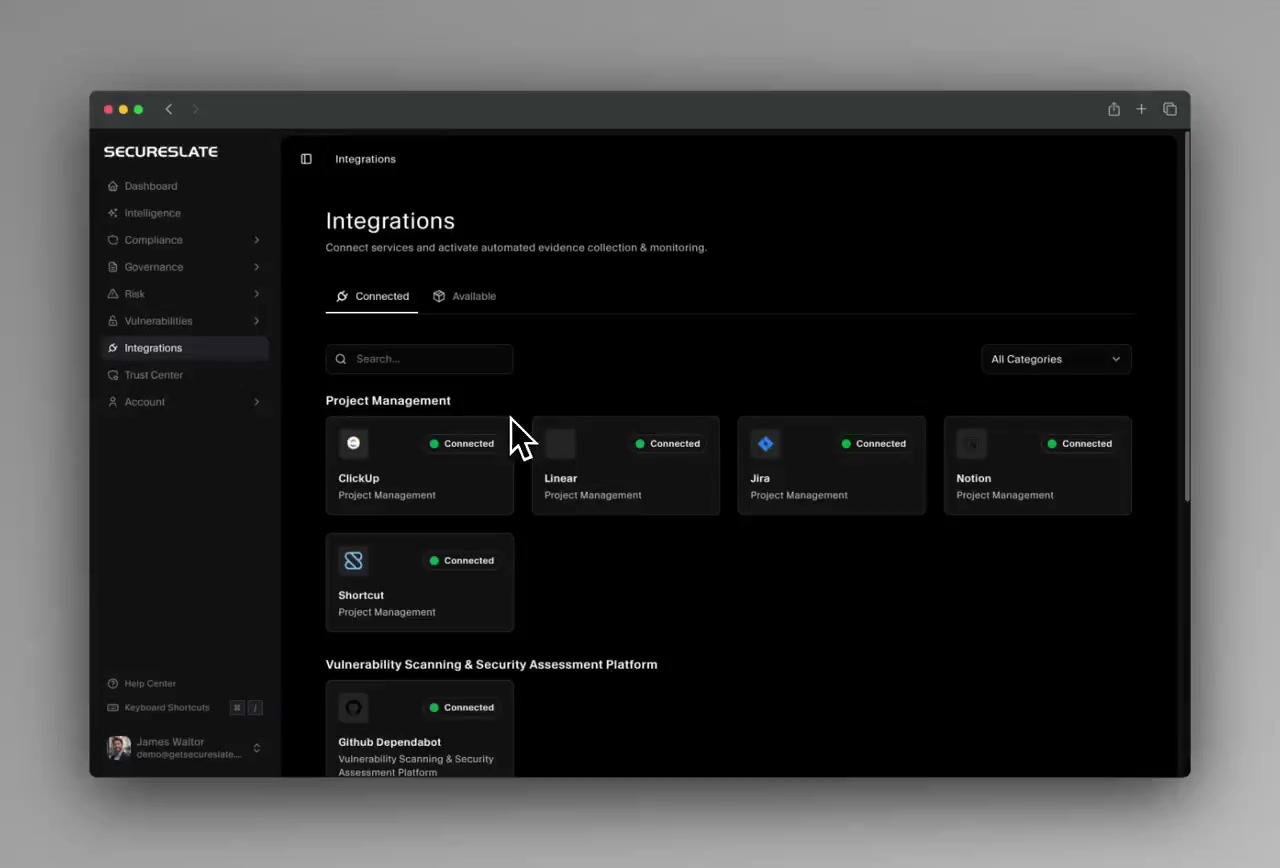
Connect your cloud provider, identity provider, code host, and devices once. Controls are tested continuously against live configuration, and when one fails, SecureSlate AI finds the gap and prepares a fix for your team to approve.

People and device controls without the chasing
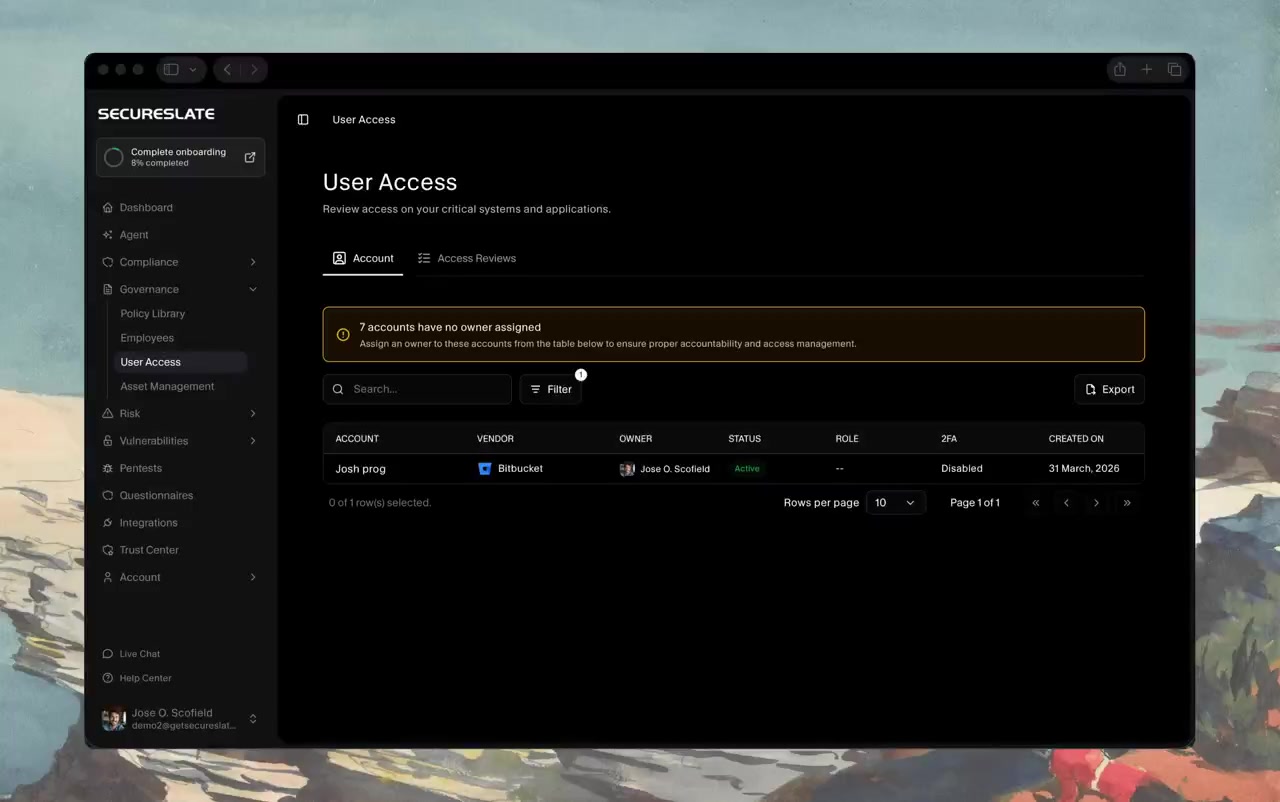
Security awareness training, access reviews, and device checks for encryption, screen lock, and antivirus run on a schedule and are tracked for you. That covers the Annex A people controls and endpoint control 8.1 with evidence an auditor can sample.

Supplier security and a Trust Center

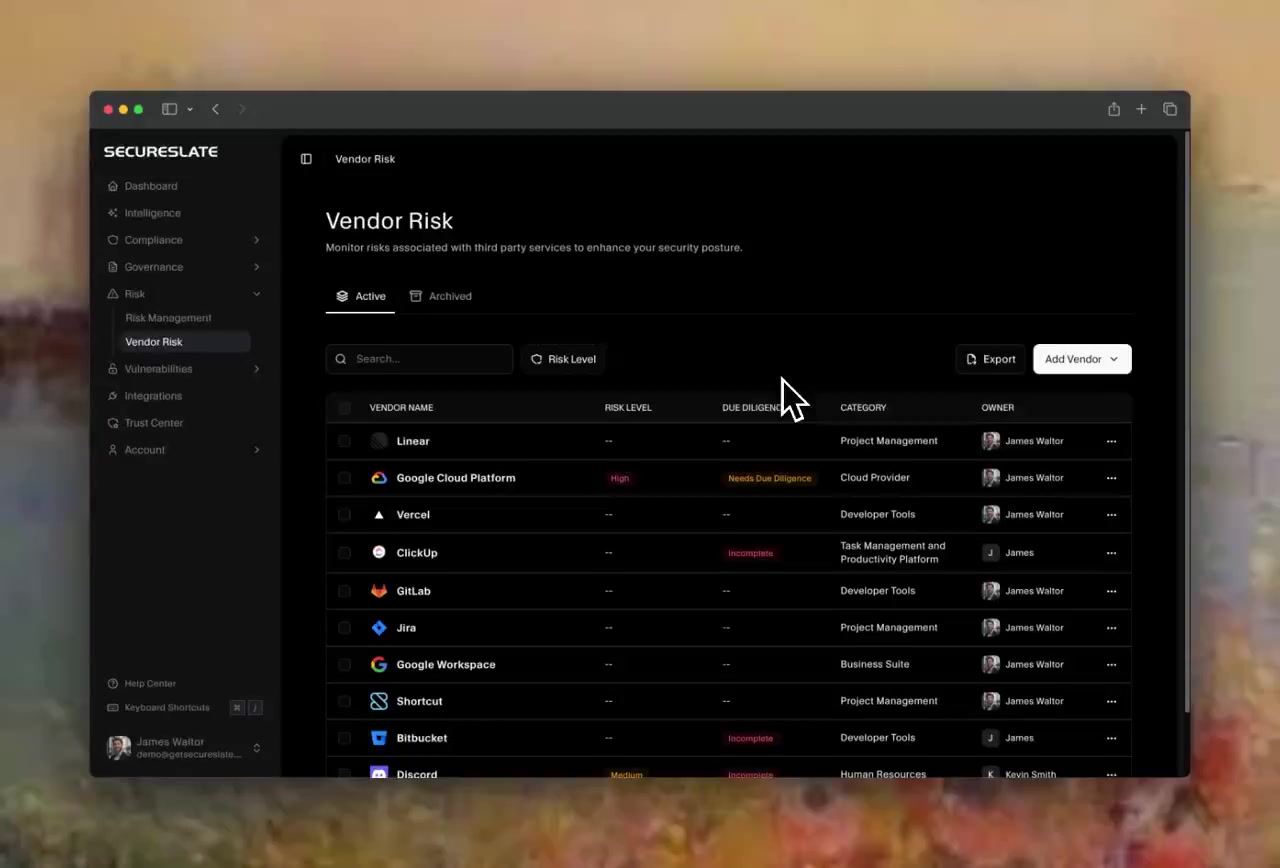
Controls 5.19 to 5.22 expect you to know what each supplier touches and to review them. We keep the vendor inventory and assessments current, then publish your certificate and posture on a Trust Center buyers can check themselves.
Annex A technological controls

ISO 27001:2022 added controls that need evidence from your code and cloud, not a policy.

Threat intelligence, cloud services, configuration management, and secure coding all arrived in the 2022 revision. Security scanning is part of the engagement, so the evidence comes from your real repositories, domains, and cloud accounts.
Annex A 8.25, 8.28

Code security scanning

Repositories scanned for vulnerable code, with findings classified by CWE, ranked by severity, and traced to the line. That shows secure coding is practised, not only written into a policy.
Annex A 5.17, 8.4

Secrets detection

API keys, tokens, and credentials committed to source code, found and pinpointed to the file and line so they are revoked before anyone else finds them.
Annex A 5.21, 5.32

Dependency and license risk

An SBOM for every repository, with the open source licenses that create obligations flagged in plain language. It answers both the ICT supply chain and the intellectual property controls.
Annex A 8.8, 8.29

Public surface monitoring

Your domains and forgotten subdomains scanned on a schedule and when you ship, with each finding explained and a fix recommended. That is the record of technical vulnerability management auditors ask for.
Annex A 5.7, 5.17

Dark web monitoring

Company email addresses checked against known breach data, with what was exposed and when. It gives threat intelligence, one of the controls added in 2022, a concrete source.
Annex A 5.23, 8.9

Cloud misconfiguration checks

AWS, Azure, and GCP configurations checked through read-only access for risky settings in encryption, access, logging, and networking, which is the evidence behind cloud service and configuration management controls.
Beyond ISO 27001

One ISMS, several certificates.

Controls built for ISO 27001 carry into the standards your buyers ask for next, so the second framework extends the program instead of starting a new one.

SOC 2

The attestation US buyers ask for. A large share of ISO 27001 controls map to the Trust Services Criteria, so the gap is mostly the report format and the observation period.

ISO 42001

The AI management system standard. It shares the clause structure of ISO 27001, so your risk, internal audit, and management review processes carry straight across.

ISO 27701

Privacy information management. Much of the access, supplier, and risk work in your ISMS applies directly once you process personal data at scale.

ISO 27017

Security guidance for cloud service providers and cloud customers, often assessed alongside your ISO 27001 audit rather than as a separate project.

GDPR

ISO 27001 covers the security of personal data that Article 32 asks for. GDPR adds lawful basis, data subject rights, and records of processing on top.

NIS 2

The EU cybersecurity directive for essential and important entities. An operating ISMS already covers much of its risk management and incident handling expectations.
Customer results

ISO 27001 results from SecureSlate customers

Non-security teams that needed ISO 27001 for their buyers and did not want the program to stall their operations.

Certified
Senbee A/S achieved ISO 27001:2022 without pausing operations for audit prep
2×
Faster audit readiness for a tech service provider after moving off spreadsheets

We always knew the next step. SecureSlate made GDPR and Cyber Essentials feel manageable for a non-security team, and we reclaimed 200+ hours while getting ready in under seven weeks.

Catherine
Catherine Director at Quality Early Years

One dashboard for the whole ISO 27001 process. It’s intuitive, saves time, and brought everything together so we could certify without slowing operations.

Tristan
Tristan CEO at Senbee A/S
Resources

Read up before your scoping call.

Practical guides to the parts of ISO 27001 teams ask about most, from the controls themselves to what the audit costs.

FAQs

What teams ask before starting ISO 27001.

Find out what your ISO 27001 certificate will take

Bring your scope and the buyer asking for it. You will leave the call with a gap summary, a timeline, and a fixed price, whether or not you work with us.

Jamie
Virtual Agent

Hi! I'm Jamie. Curious about your current compliance challenges and how automation might help your team?